Security & Compliance
Multi-Layered Security Model
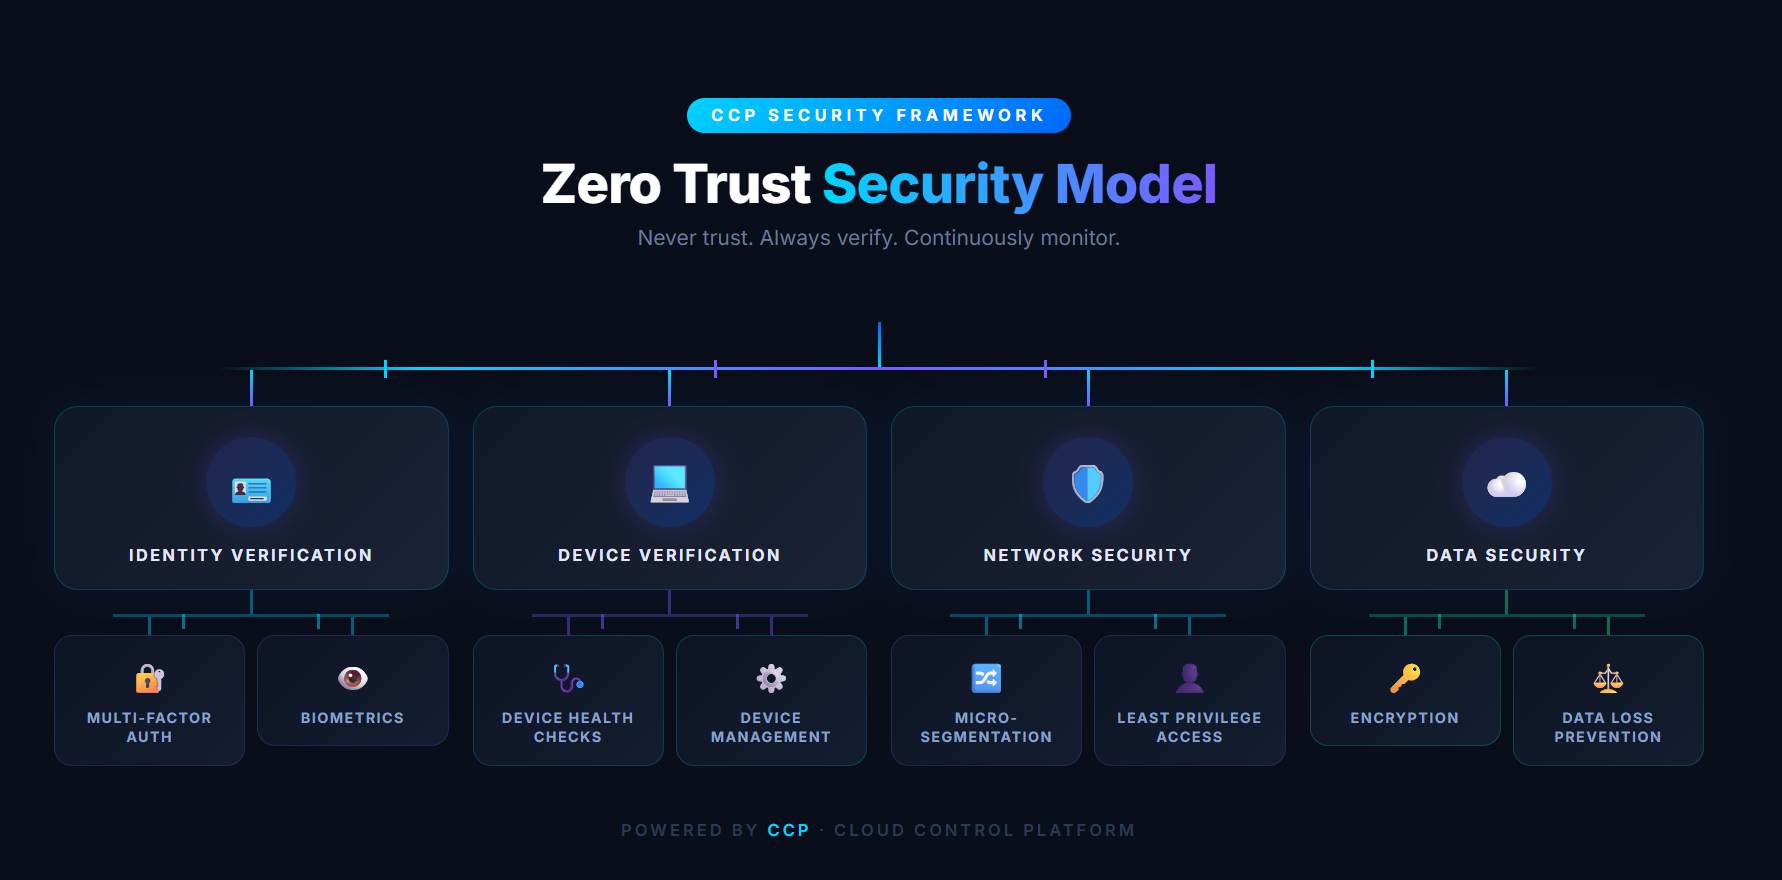
CCP implements defense-in-depth with a multi-layered security posture. Every request passes through authentication, authorization, encryption, and audit controls — no action is trusted by default. Security is not an add-on; it is built into every layer of the platform from the IAM engine to the storage tier.
| Security Layer | Mechanism | Protection |
|---|---|---|
| Authentication | Keycloak v24.0.5 — OAuth2/OIDC | Identity verification for every user and service interaction |
| Authorization | OpenFGA, pre-defined RBAC roles at Tenant and Project levels | Role and context validation on every resource action |
| Transport Encryption | mTLS (Mutual TLS) between all services | Encrypted communication and mutual service authentication |
| At-Rest Encryption | AES-256 for all stored data | Data protected against unauthorized physical or logical access |
| Identity Federation | SAML 2.0 with Microsoft ADFS and Entra | Seamless SSO with enterprise identity providers; no password replication |
| Tenant Isolation | Per-tenant Keycloak realm | Complete identity and session isolation between tenants |
| Network Security | VPC isolation, Firewall, NAT Gateway | Network-level tenant segregation and perimeter protection |
| Audit Logging | API gateway logs, SIEM integration, centralized log management | Full traceability of every action; immutable audit trail |
| Security Services | WAF, SIEM, CSPM, DDoS protection, Cloud HSM, SSL management | Perimeter and workload-level threat detection and protection |
Identity and Access Management
Keycloak IAM Engine
CCP provides granular, policy-driven access controls to govern user actions across managed environments. CCP leverages Keycloak as its core Identity and Access Management engine, bringing enterprise-grade authentication and identity federation capabilities natively into the platform.
Role-Based Access Control (RBAC): Fine-grained permissions based on user roles (e.g., Administrator, FinOps Analyst, Auditor, DevOps Engineer) enforce the Principle of Least Privilege.
Multi-Tenancy & Account Isolation: Logical separation of tenant environments prevents cross-tenant data leaks or unauthorized cross-account configuration changes.
Audit Logging: Immutable, tamper-evident audit logs record every identity-driven action and API request for full traceabilty.
Enterprise Identity Federation: Seamless integration with enterprise identity providers via SAML 2.0 and OpenID Connect (OIDC), enabling support for Microsoft Entra ID (Azure AD), Okta, Ping Identity, and Google Workspace.
Single Sign-On (SSO) & Social Login: Streamlined SSO workflows across all CCP services alongside configurable social login options for developer environments.
Adaptive Multi-Factor Authentication (MFA): Enforcement of TOTP (Time-based One-Time Password), SMS, WebAuthn/FIDO2 hardware keys, and contextual step-up MFA based on risk scoring.
User Session & Realm Management: Multi-realm isolation allows individual organizations/tenants within CCP to manage their own local users, credential policies, and session lifetimes independently.
OpenFGA Authorization Engine
Authorization is enforced through OpenFGA, Coredge's fine-grained authorization engine. OpenFGA implements a relationship-based access control (ReBAC) model that evaluates permissions based on roles, relationships, and context — not just flat role assignments.
End-to-End Encryption
CCP enforces strong cryptographic standards across all data states to maintain strict confidentiality and integrity.
| Data State | Standard / Implementation | Details |
|---|---|---|
| Data in Transit | TLS 1.3 / mTLS | All external communications, API endpoints, and internal microservice-to-microservice traffic use Mutual TLS (mTLS). |
| Data at Rest | AES-256 | Database instances, object storage, and configuration state stores are encrypted using industry-standard AES-256 encryption. |
Compliance Alignment
CCP is designed with compliance requirements of government and regulated industries in mind.
| Compliance Area | CCP Implementation |
|---|---|
| Access Control | Keycloak IAM with RBAC (OpenFGA), per-tenant realm isolation, least privilege via 18 pre-defined roles |
| Cryptography | mTLS in transit, AES-256 at rest, Cloud HSM for key management |
| Audit & Accountability | API gateway audit logs, SIEM integration, centralized log management with long-term retention |
| Identity & Authentication | MFA, SAML 2.0 federation, SSO, session management, short-lived tokens |
| Data Sovereignty | On-premises deployment, local data residency, geo-replicated backups within defined regions |
| Workload Protection | CSPM, WAF, firewall per tenant, per-cell network isolation via VPC |